Dark Web & Stealer Intel
Scanning breach dumps and infostealer logs.
Introducing Tiora:
Tool execution modules
Scanning breach dumps and infostealer logs.
Analyzing exposed domains and services.
Cross-referencing MISP and threat feeds.
Tracking active extortion groups and TTPs.
Tiora: Correlation complete. Detected compromised corporate credentials linked to exposed external RDP service. Automated triage alert generated.
The purpose-built cyber threat AI agent that unifies attack surface monitoring, dark web intelligence, and automated investigation across your entire enterprise.
Request a DemoThe Tiora architecture
With multi-tool async orchestration
 Agent StateReason · route · respond
One reasoning layer connects every external telemetry source, intelligence feed, and remediation action into a single investigation flow.
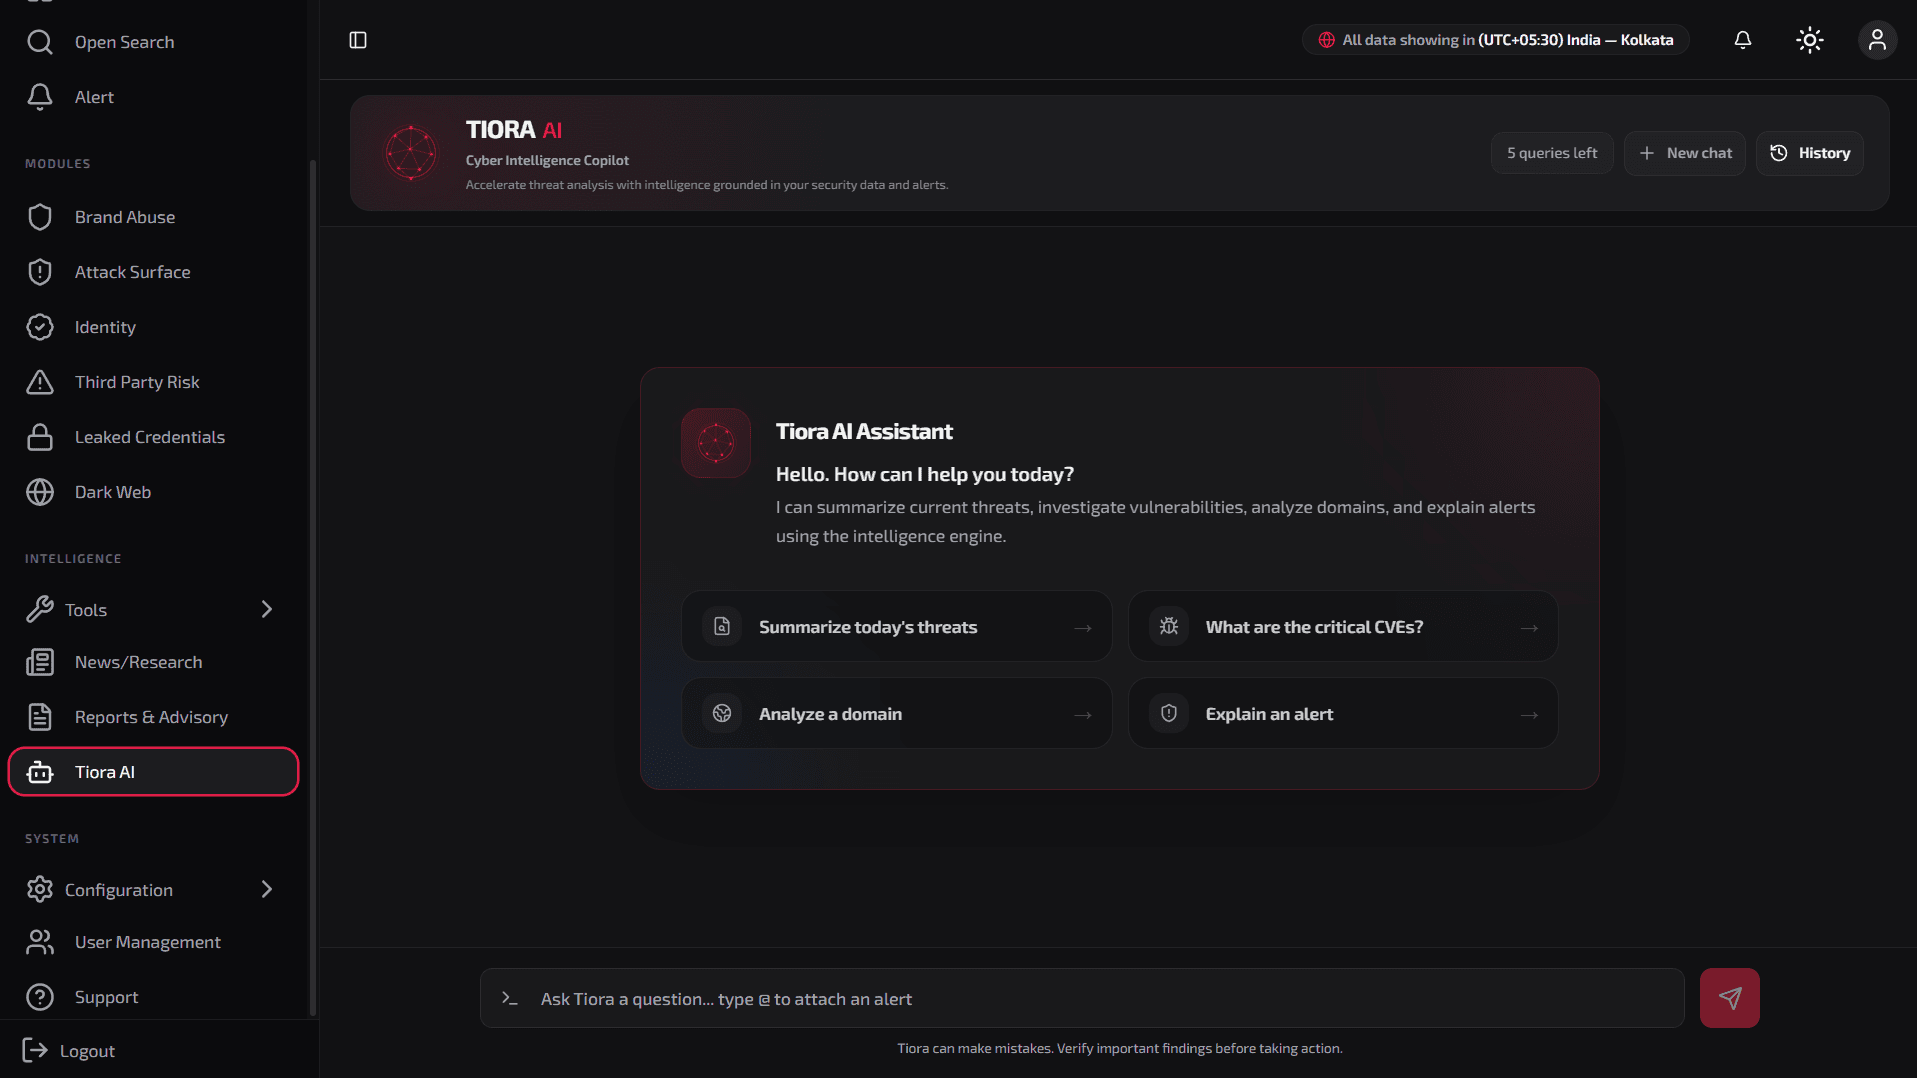
Move from a high-level signal to the full story with conversational, context-rich analysis.
Explore investigationHow Tiora works
Query any asset, domain, or threat actor. Get deep correlation across your entire external exposure profile in seconds.
Tiora AI
AI-powered investigation workflow
Continuous telemetry from dark web, ASM, and breach feeds
Graph reasoning maps threats to your assets & watchlists
Autonomous multi-tool analysis and exposure scoring
Actionable alert dispatch to Jira, Slack, Teams & SOAR
Human + AI workflow
New intelligence enters the workflow from your connected security sources.
Security teams define watchlists, critical assets, and mission priorities.
Autonomous AI cross-references dark web dumps, ASM assets, and threat feeds.
Human analysts verify high-impact discoveries and request deep investigations.
Teams dispatch containment actions directly to SIEM, SOAR, and ticketing queues.
Approved actions are delivered to the teams and systems that resolve the threat.
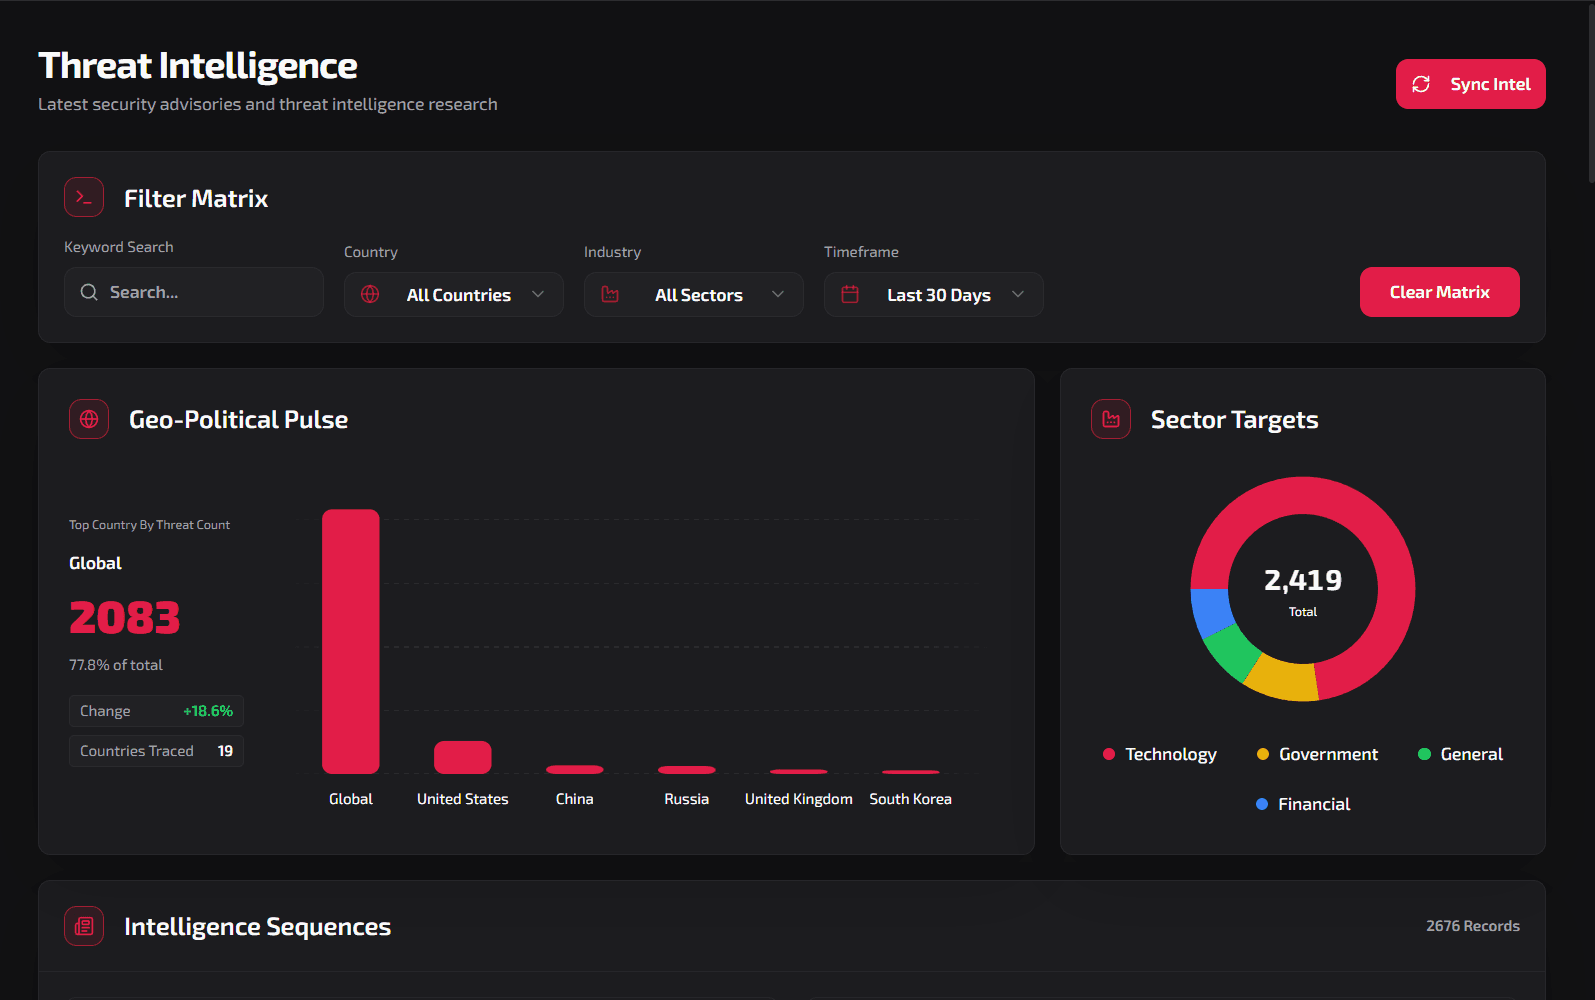
Global threat intelligence
Connect signals from everywhere and see what matters as it happens.
Tiora AI
Experience autonomous threat correlation and AI-driven investigation. Request a personalized demo of Tiora AI.